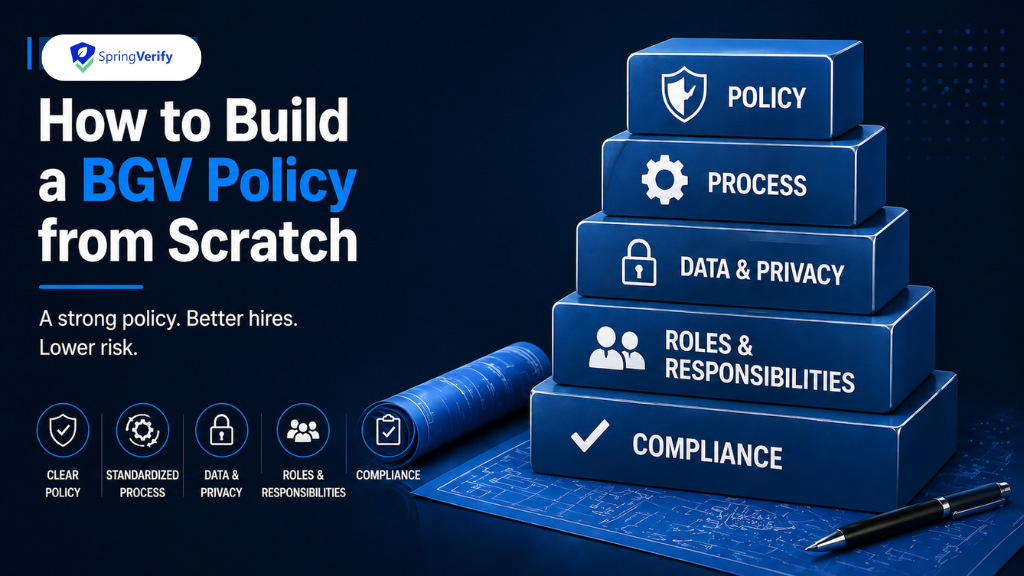
Your company just hit 200 employees. An enterprise client asks during a vendor assessment: “Can you share your background verification policy?” You look at your HR head. Your HR head looks at you. Neither of you has one. You have a practice — “we usually run checks through SpringVerify before people join” — but you don’t have a policy. And that gap just cost you a deal worth Rs. 2 crores annually.
A practice is what you do when you remember. A policy is what you’ve committed to doing, documented, approved by leadership, and can be audited against. When Deloitte or Accenture sends a vendor compliance questionnaire, they don’t ask about your practices. They ask for your policy document — signed, dated, and comprehensive.
Define exactly who gets screened. All employees? Contractors? Interns? Board advisors? Gig workers?
A strong scope statement: “All individuals engaged by [Company Name] in any capacity — including full-time employees, fixed-term contractors, interns, consultants, and board advisors — shall undergo background verification appropriate to their role and access level prior to or within 15 business days of commencement.”
Not every hire at your Bangalore office needs the same checks as your Mumbai CFO. Define 3-4 tiers:
Tier 1 — Standard (all hires): Identity (Aadhaar/PAN) + Criminal database + Address verification. Cost: Rs. 300-500.
Tier 2 — Professional (white-collar): Tier 1 + Education + Employment (last 2 via EPFO + HR outreach). Cost: Rs. 800-1,200.
Tier 3 — Sensitive (finance, data, client-facing): Tier 2 + Credit check + Reference checks + Extended employment (last 3-5 employers). Cost: Rs. 1,200-1,800.
Tier 4 — Executive (CXO, board): Tier 3 + MCA directorship search + Litigation screening + Media screening + Global sanctions. Cost: Rs. 3,000-5,000.
Map every role in your organization to a tier. A Keka or Darwinbox role master can tag the BGV tier to each job code.
Document: how consent is obtained (digital via WhatsApp/portal, with vernacular options for blue-collar candidates), what specific data is collected and for what purpose (DPDPA Section 4), retention period (recommend 3 years for standard roles, 8 years for BFSI per RBI guidelines), deletion process after retention period expires, and how candidates exercise correction and deletion rights under DPDPA Sections 12-13.
When a check returns a discrepancy: who gets notified (HRBP + hiring manager + Legal for red flags), severity classification (critical/major/minor — predefine which discrepancies fall in each), candidate notification within 2 business days with specific findings, candidate response window of 5-7 business days, decision authority (HRBP for minor, VP HR for major, VP HR + Legal for critical), and documentation requirements at each step.
Mistake 1: Making exceptions for “urgent hires” and never going back to complete the check. Fix: no exceptions without VP-level written approval and a 15-day completion deadline.
Mistake 2: Running the same checks on every hire regardless of role. Fix: tiered packages save 30-40% in BGV costs.
Mistake 3: No annual policy review. Fix: calendar a review every January. Regulations change (DPDPA rules are still evolving), and your policy must keep up.
Mistake 4: Not defining what happens with amber cases. Fix: include maximum hold periods (10 days standard, 15 days sensitive, 20 days executive).
Mistake 5: Keeping the policy in a Google Doc nobody reads. Fix: embed it in your HRMS onboarding workflow. Make it a mandatory acknowledgment for every hiring manager.
Name your BGV vendor. Specify SLAs (TAT by check type, amber rate caps, breach notification timelines). Require SOC 2 Type II and ISO 27001 certifications. Define annual vendor reviews with specific metrics. Include escalation contacts.
Annual policy review by VP HR + Legal. BGV completion records retained for defined period. All documentation producible within 48 hours for client or regulatory audits. Quarterly vendor performance reviews.
Print it on company letterhead. Have the CEO sign it. Date it. This document serves triple duty: investors ask about governance (show this), enterprise clients audit your processes (share this), DPDPA regulators check compliance (produce this). A signed BGV policy is worth more than ten vendor certifications.
SpringVerify’s platform supports all four verification tiers with configurable check packages, DPDPA-compliant WhatsApp-based consent collection, and audit-ready reporting — making it easy to operationalize the policy you’ve just built.
Key Takeaways: